M. Shaheer
● Riyadh, Saudi Arabia · 14+ years in network security

I decide who and what gets onto the network.

CISSP-certified Network Security Consultant with 14+ years across networking and cybersecurity. I architect and operate NAC, firewall, WAF and Zero Trust stacks for government, banking and critical-infrastructure organisations.

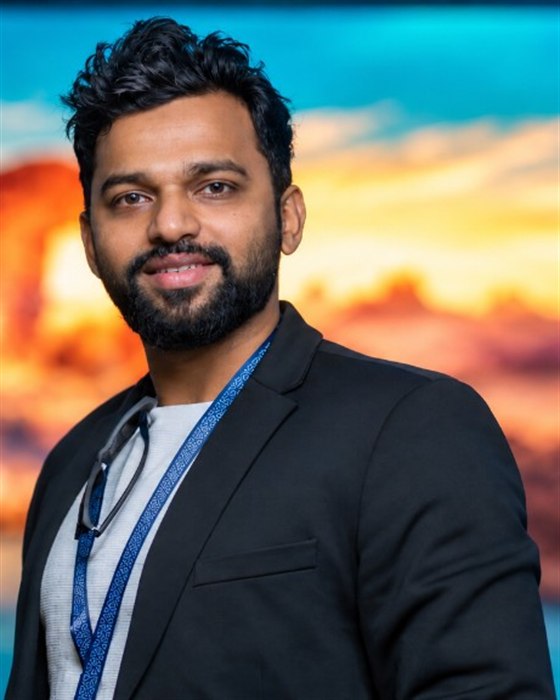
Muhammed Shaheer in a black blazer against a sunset backdrop
Access-Accept ✓
profile: CISSP · ZT
0
years in network & security engineering
0
bank branches moved onto NAC
0
IT/OT assets under central access control
0
uptime on NAC high-availability design
scroll
01 · About

I learned where integrations break by testing them from the inside.

I'm a CISSP-certified Network Security Consultant based in Riyadh, with 14+ years across networking and cybersecurity. I architect and operate multi-vendor security for government, banking and critical-infrastructure organisations in Saudi Arabia — the Fortinet Security Fabric, Palo Alto NGFW, Forescout NAC, Ivanti NAC and VPN, F5 BIG-IP and Splunk SIEM, plus Opinnate, Seclore DRM and Riverbed APM.

I started in 2011 on Cisco and Juniper switching and routing, then spent four years at Juniper Networks and four more at Pulse Secure (Ivanti) validating how NAC, VPN, firewalls and SIEMs behave together. Since 2020 I have been on the deployment side: NAC across 300+ Bank Al Bilad branches, a 14-appliance Forescout estate covering 10,000+ endpoints for TAHAKOM, and today a multi-vendor Zero Trust stack for SPGA at Starlink.

Education

Anjuman Engineering College, Bhatkal

B.E. · Visvesvaraya Technological University, Belgaum · 2005–2009
Languages
English (Professional) · Arabic (Fluent)
Hindi (Fluent) · Malayalam (Native)
Engagement
Saudi Engineering Council (SEC) registered
ISC² chapter member & speaker · Bangalore, Dubai
IT Wing Lead, Kerala Engineers Forum Riyadh · 1,500+ engineers
How I work
Think Security.Build Resilience.Lead with Zero Trust.
Zerobreaches across the banking network
85%less unauthorised lateral movement
30%lower MTTR after root-cause work
35%leaner firewall rule base
14Forescout appliances, multi-region
98%SLA adherence on incident response
40%smaller storage footprint
2,000+users in security operations scope
60%less manual testing through automation
1,000+users on a secure LAN I designed
02 · Selected work

Deployments, one big number each.

/01
0
smaller firewall rule base
Jul 2023 to present · Starlink · SPGA

Multi-vendor security for a government authority

Architecture and operations for SPGA, a Saudi government authority with 2,000+ users. Fortinet Security Fabric, Palo Alto NGFW, Forescout NAC, Ivanti VPN, F5 BIG-IP and Netskope, aligned to Zero Trust and NCA requirements. FortiSandbox across HQ, DC and branches, a 3-tier F5 design, and Seclore to protect documents beyond the perimeter.

FortiSandboxSeclore EDRMF5 · 3 tiersOpinnate
/02
0
IT/IoT/OT endpoints · 14 appliances
Jul 2023 to present · Starlink · TAHAKOM

NAC and FortiGate fabrics deployment for large Government Sectors

A 14-appliance Forescout estate across KSA regions for TAHAKOM, covering smart mobility and national critical infrastructure. Previously unmanaged laptops, phones, printers, cameras, NVRs and sensors became a reportable inventory, with graduated policies for fragile OT devices.

−85% lateral movement−30% MTTRZero Trust segmentation
/03
0
branches on NAC · 99.99% uptime
Sep 2020 to Jul 2023 · Security Matterz · Bank Al Bilad

Bank-wide network access control

802.1X for managed endpoints and MAB for ATMs and POS terminals across Bank Al Bilad's branch network. Active-passive failover between the primary DC and DR, Splunk SIEM integration, dynamic VLANs and posture-based quarantine.

0 breaches−35% endpoint incidents−40% storage98% SLA
/04
0
faster customer reviews
2012 to 2015 · Juniper Networks

Junos Node Unifier (JNU)

A central management layer to configure, monitor and upgrade many Junos platforms from one MX Series router. Tested for AT&T, Verizon and Comcast. The team received CEO appreciation.

CEO appreciationMX SeriesSLAX · Perl
03 · Experience

Fourteen years, from the test lab to the bank floor.

Jul 2023 to present · 3 yrs 4 mos

Cybersecurity Consultant, Technical Lead

Starlink
Riyadh, Saudi Arabia · On-site · government and critical infrastructure

SPGA — current engagement

Saudi government authority · 2,000+ users
  • Architect and operate an integrated stack — Fortinet Security Fabric, Palo Alto NGFW, Forescout NAC, Ivanti VPN, F5 BIG-IP and Netskope — aligned with Zero Trust and NCA requirements.
  • Manage FortiGate and Palo Alto firewalls, including policies, SSL inspection, IPS/IDS and traffic shaping, with centralised management through FortiManager.
  • Audited the firewall rule base and cut it by 35% by retiring unused and over-permissive rules.
More details
  • Integrated Opinnate across the firewall estate for policy visibility, analysis and rule-base governance.
  • Manage FortiWeb WAF — custom rules, false-positive tuning, Active/Passive HA and firmware upgrades — and lead CVE response for perimeter devices.
  • Deployed FortiSandbox across HQ, DC and branches with 24/7 monitoring, and enforce daily IOC-based blocking on firewalls and the Netskope proxy.
  • Analyse logs in FortiAnalyzer with the SOC, and lead weekly SOC governance using threat intelligence and NCA feeds.
  • Delivered Forescout as a high-availability failover cluster for 2,000+ users.
  • Designed a 3-tier F5 BIG-IP load-balancing architecture across the internal DC and DMZ.
  • Architecting the Seclore enterprise DRM deployment so sensitive documents stay protected beyond the perimeter.
  • Integrated Riverbed APM for application performance and latency visibility.

TAHAKOM — previous engagement

Smart mobility and national critical infrastructure
  • Designed, deployed and operated 14 Forescout CounterACT appliances across multiple KSA regions, with visibility over 10,000+ IT, IoT and OT endpoints.
  • Discovered and classified unmanaged assets — laptops, VoIP phones, printers, cameras, NVRs and sensors — and applied graduated policies to fragile OT devices.
  • Designed Zero Trust segmentation with NAC and NGFW controls, reducing unauthorised lateral movement by 85%.
More details
  • Built custom Forescout classification rules for proprietary equipment and asset-specific baselines.
  • Integrated Forescout with Palo Alto firewalls and Cisco switches for risk-based segmentation.
  • Engineered REST API integrations with Palo Alto and antivirus platforms for automated quarantine.
  • Led incident-response simulations and OT tabletops; root-cause analysis reduced MTTR by 30%.
  • Resolved tickets with Wireshark, tcpdump and CLI tooling, and built prioritised remediation plans from vulnerability assessments.
  • Delivered executive dashboards on asset inventory, risk posture and remediation, plus knowledge transfer for handover.
ForescoutFortiGateFortiAnalyzerFortiManagerFortiWebFortiSandboxPalo AltoF5 BIG-IPIvanti VPNNetskopeOpinnateSecloreRiverbedSplunk
Sep 2020 to Jul 2023 · 2 yrs 11 mos

Cybersecurity Resident Engineer

Security Matterz · Client: Bank Al Bilad
Riyadh, Saudi Arabia · On-site
  • Led end-to-end NAC deployment across 300+ bank branches, using 802.1X for managed endpoints and MAB for ATMs and POS systems.
  • Designed active-passive HA failover between the primary DC and DR, reaching 99.99% uptime with synchronised profiler databases and automated failover.
  • Recorded zero security breaches across the banking network during my tenure.
More details
  • Integrated NAC with Splunk SIEM through custom parsers, correlation searches and automated response workflows across 300+ locations.
  • Built dynamic VLAN assignment, ACL enforcement and real-time posture-based quarantine for compliance validation.
  • Reduced storage footprint by 40% through automated database maintenance and archival, while keeping audit compliance.
  • Held 98% SLA adherence for security incident response through streamlined escalation workflows and proactive monitoring.
  • Reduced endpoint security incidents by 35% across 300+ remote branches.
  • Upgraded cluster appliances through critical migrations and took part in BCP failover testing with IT and business units.
802.1XMABRADIUSProfilerSplunkPalo AltoGuest Captive PortalIvanti IPSOWASPWireshark
Dec 2016 to Sep 2020 · 3 yrs 10 mos

Senior Security Solutions QA Engineer

Pulse Secure (Ivanti)
Bengaluru, India · On-site
  • End-to-end solution testing and interoperability validation of Ivanti NAC/VPN with Cisco, Juniper, HP, Dell, Arista, Fortinet, Palo Alto, Check Point and Splunk.
  • Delivered proof-of-concept implementations for Fortune 500 clients and government agencies, with solution sizing and architecture recommendations.
  • Benchmarked against Cisco ISE, Cisco ACS, Aruba ClearPass and Forescout to shape Ivanti's NAC positioning and roadmap.
More details
  • Tested RADIUS, 802.1X, MAB, TACACS+, SNMP-based ACL/VLAN enforcement, guest access and advanced secure access scenarios.
  • Built and validated topologies with site-to-site VPN, admission control and identity management workflows, integrating Ivanti with next-gen firewalls and SIEMs.
  • Led development of Splunk dashboards, correlation rules and automated response workflows using Pulse Secure syslogs.
  • Ran security validation with Burp Suite, IBM AppScan, NMAP and Codenomicon protocol fuzzing before release. Awarded “Best Performer” by the engineering team.
  • Drove device profiling and visibility testing through SNMP polling, DHCP fingerprinting, NMAP and WMI.
  • Built integrations using IF-MAP, a REST API and WebSockets to bridge NAC and VPN.
JenkinsHost-CheckingBurp SuiteCheck PointThreat ModelingAristaTACACS+Perl
May 2012 to Dec 2016 · 4 yrs 8 mos

Juniper Networks

Three roles across RBU and CDBU
Bengaluru, India · On-site

Senior QA Test Engineer, CDBU

Oct 2015 to Dec 2016
  • Led feature validation of Native Analyzer technologies: SPAN, RSPAN, ERSPAN and firewall-filter port mirroring (PACL, VACL, RACL).
  • Built VMware testbeds, reproduced customer issues and worked with JTAC on root-cause analysis.

Senior QA Engineer, security features

May 2012 to Nov 2016
  • Designed test automation frameworks for security features on EX, MX and SRX using the JT framework and Perl, cutting manual testing by 60%.
  • Led validation of 802.1X, TACACS+, RADIUS, port mirroring and storm control for enterprise deployments.
  • Built lab topologies (L2/L3 VPN, OSPF, BGP, MC-LAG, RSTP/VSTP) for security testing and customer proofs of concept.

Network Test Engineer, RBU

May 2012 to Oct 2015
  • Demonstrated Junos Node Unifier as a key Junos enhancement, giving a 30% boost in customer review efficiency. The team received CEO appreciation.
  • Led testing and lifecycle management of JNU packages for AT&T, Verizon and Comcast.
JNCISJNCIPSLAXPerlBGPOSPFMC-LAGMX240 / MX480
Feb 2011 to Apr 2012 · 1 yr 3 mos

Senior Software Engineer (Network Security)

Paxterra Software Solutions
Bengaluru, India · On-site
  • Designed and maintained a secure LAN for a 1,000-user enterprise with VLAN segmentation, ACLs and structured IP addressing.
  • Configured RIP, EIGRP and OSPF, and implemented SNMP/NetFlow monitoring with custom alerting for traffic and capacity analysis.
More details
  • Tested Cisco 3750 and 1800 platforms, including negative testing of 802.1X, MAB, MDA and port security, and L2/L3 protocols on Juniper MX.
  • Used Wireshark and tcpdump for packet analysis and debugging on Linux.
  • Started test automation in TCL, and automated repeatable test cases with Perl and IXIA.
CiscoJuniperTCLPerlIXIAWiresharktcpdump
04 · Skills

The stack, grouped by what it protects.

05 · Certifications

Credentials, with the clock running.

Earned & registered

  • Cisco Certified Network Professional (CCNP)Cisco · 2016
  • Cisco Certified Network Associate (CCNA)CSCO11668234
  • Juniper Networks Certified Internet Specialist, SPJPR133589
  • Juniper Networks Certified Internet Associate (JNCIA-M)Juniper
  • Pulse Secure NAC Expert (Ivanti)Ivanti
  • Saudi Engineering Council (SEC) registeredSEC
  • Session on Security and Risk ManagementCyberFrat · 2026

In progress

  • Certified Information Systems Auditor (CISA)ISACA
  • BeyondTrust PAMIn progress
  • Master’s in Artificial IntelligenceIn progress

Previously held

  • Forescout Certified Associate (FSCA)2023–2025
  • Splunk Core Certified Power User2023–2026
  • Certified Technical Expert, Pulse Policy Secure2022–2024
06 · Contact

Need NAC, Zero Trust or security operations done properly?

I'm based in Riyadh and work with government, banks and critical-infrastructure organisations across the region. Email or call, or download the resume.

◎ Riyadh, Saudi Arabia · mshaheerkp@gmail.com · +966 54 882 8992
Link copied